Tested.Protected.Audit-ready.
Security testing, compliance, advisory and managed security — from one in-house team.
Attackers are faster than ever. So are we.
New flaws are exploited in days and audits keep getting stricter. HostX finds your risks, helps you fix them and gets you audit-ready — faster, with AI platforms behind every service.
Attacks per organisation per week in India
Threat IntelFrom CVE disclosure to live in-the-wild exploitation
Exploit VelocityAverage cost of a data breach across enterprises in India
IBM Security ReportHostX SOC coverage every minute of the year
Always Active
One team that tests, protects and proves your security. End to end.
Our in-house experts test your apps, networks and cloud like real attackers, watch your environment around the clock, and get you ready for ISO, SOC 2, RBI, SEBI and IRDAI audits.
Across 6 practice areas
Across banking, manufacturing, healthcare and accounting
From first call to full coverage, without the guesswork.
Consultation
We map your assets, your risk history, and what "compliant" looks like for your team.
Scoping & Assessment
Vulnerability scans and penetration tests run against your real environment, asset by asset.
Remediation & Beyond
You get your report and fixes verified, and HostX keeps watching for new risk from day one onward.
Explore→Consultation
We map your assets, your risk history, and what "compliant" looks like for your team.
Scoping & Assessment
Vulnerability scans and penetration tests run against your real environment, asset by asset.
Remediation & Beyond
You get your report and fixes verified, and HostX keeps watching for new risk from day one onward.
Explore→The platforms behind our services.
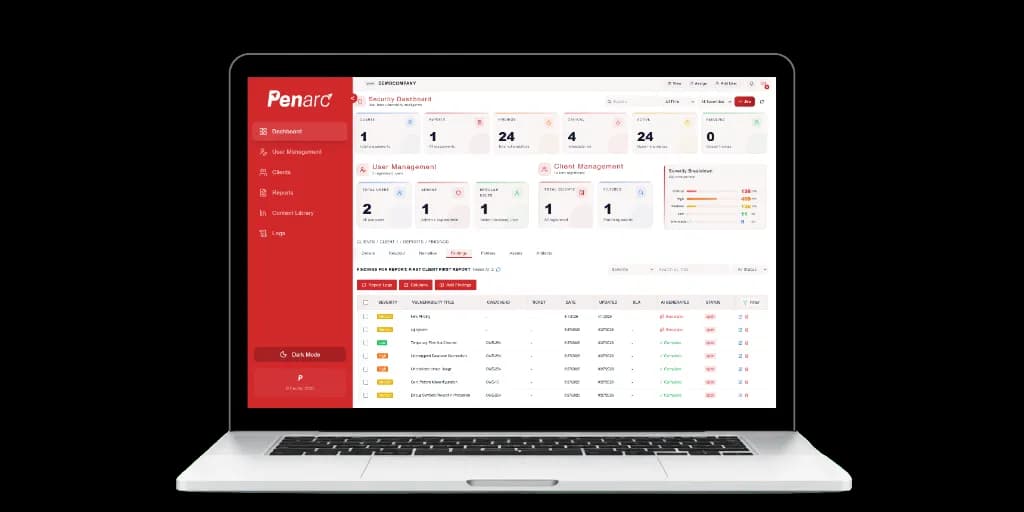
Pentest reports in one click.
Testers log findings as they work. Penarc's AI fills in the description, business impact, solution, references and CWE/CVE for every finding, then exports a polished, branded PDF ready for your client.
Whatever you're securing, we monitor, test and prove it.
SOC, offensive security, and regulatory compliance unified under one expert team so nothing slips through the cracks.
Managed SOC & Detection
In-house L1–L3 analysts watch logs, endpoints, and cloud 24/7/365 to hunt threats and contain breaches in minutes.
- ✓24/7/365 active monitoring
- ✓MDR with automated host containment
- ✓Incident response hotline with 15-min SLA
Offensive Security
Rigorous manual penetration testing across web apps, mobile, APIs, networks, and cloud infrastructure plus red teaming.
- ✓OWASP Top 10 & WSTG methodology
- ✓Adversary emulation & red teaming
- ✓Free re-test & certified patch verification
Application Security
Identify security vulnerabilities before code hits production with SAST, DAST, SCA dependency scanning, and threat modeling.
- ✓Automated CI/CD pull-request scanning
- ✓Code-level fix recommendations
- ✓Full SBOM generation & CVE tracking
Advisory & Response
Executive cybersecurity leadership, vCISO advisory, cloud architectural audits, and crisis management.
- ✓Virtual CISO (vCISO) advisory
- ✓Cyber Crisis Management Plan (CCMP)
- ✓Board-level risk and posture reporting
Global Compliance
ISO 27001, SOC 2 Type II, PCI-DSS, HIPAA, and GDPR readiness with live control evidence syncing in the Compliance Tool.
- ✓Automated gap assessments
- ✓Continuous policy & evidence tracking
- ✓End-to-end auditor liaison support
India Regulatory Audits
RBI IT framework, SEBI, IRDAI, and India Digital Personal Data Protection (DPDP) Act assurance.
- ✓RBI / SEBI / IRDAI compliance audits
- ✓DPDP Act readiness & data localization
Results, not promises.
How HostX protects mission-critical systems across banking, fintech, and high-growth SaaS.
"HostX's SOC caught the unauthorized lateral intrusion at 2 a.m. and had the infected host isolated before our team even woke up."
Head of IT Security
Leading NBFC · Mumbai"We went from zero to SOC 2 Type II assurance in twelve weeks. The Compliance Tool made evidence collection organized and stress-free."
Chief Technology Officer
Enterprise SaaS Platform"Their offensive team found 42 critical logical flaws before our annual RBI audit, and Penarc reports meant our developers knew exactly how to fix them."
Chief Information Security Officer
Scheduled Commercial BankRansomware attack contained from first lateral alert
Full SOC 2 Type II audit readiness from zero
Critical design vulnerabilities remediated before RBI audit
OUR ACCREDITATIONS & CERTIFICATIONS
 ISO 9001:2015
 ISO/IEC 27001:2022
 ISO/IEC 27017:2015
 ISO/IEC 27018:2019
 GDPR Compliant
 MSME (Udyam) Registered
 Startup India Recognised
Here for you.Here for what's next.
See what zero critical findingslooks like on your own environment.